Loading...

Loading...
As of October 2026, the AI SOC Agents with the most public evidence of working on an existing XDR platform are Simbian, Intezer, Dropzone AI, CrowdStrike Charlotte AI, and Microsoft's Security Alert Triage Agent. Native Agents work best on their own vendor's data. A vendor-neutral Agent reads identity, email, cloud, and SIEM evidence, then acts through the XDR with approval.
Your XDR probably shipped with an Agent already. Falcon has Charlotte AI, SentinelOne has Purple AI, Defender XDR has Security Copilot Agents, and Cortex XDR has Cortex AgentiX.
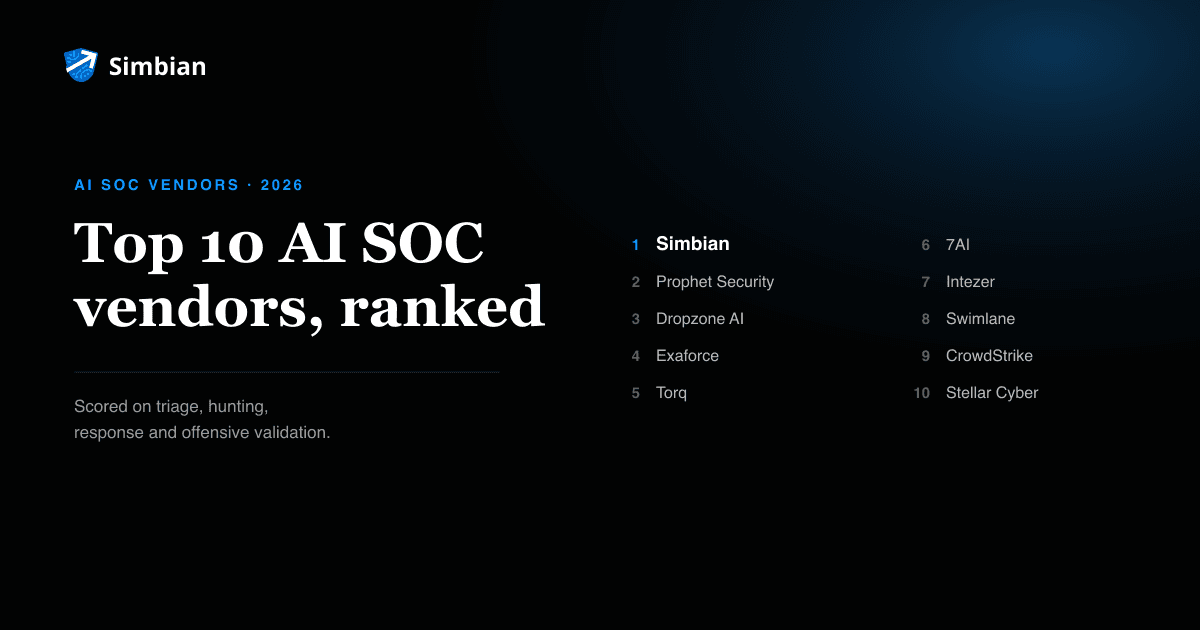
We ranked five by how many XDRs each documents writing back to. We make Simbian. It ties Intezer at four, and we put ours first. Each Agent claim below, ours too, rests on its vendor's own docs as of October 2026.
No. For most SOCs, an XDR platform's native Agent is not enough, because it reasons best over its own vendor's telemetry. Evidence from another vendor's identity, email, SaaS, or EDR tools usually has to be brought into that platform first, through its SIEM, data lake, or connectors, so the loop from alert to containment runs on one vendor's stack.
The vendors' own docs draw that boundary. CrowdStrike says Charlotte AI Detection Triage "automatically evaluates first-party security detections." Microsoft scopes its triage Agent to Defender alerts. SentinelOne's Purple AI "runs on telemetry already in the platform," third-party data included.
In March 2026, one SentinelOne admin on Reddit piped Entra telemetry into the XDR and found "those are all individual alerts with no correlation." Closing the loop takes an Agent that reads everything you already run and acts back into it.
Keep the native Agent on if you like. Decide which Agent closes each alert type, so the two don't race.
An AI SOC Agent integrates well with an XDR platform when it acts back through the XDR's response APIs with a named approver, pulls evidence from outside the XDR, covers more than one XDR from a single queue, and writes its reasoning back to the XDR's own incident.
Simbian, Intezer, Dropzone AI, CrowdStrike Charlotte AI, and Microsoft's Security Alert Triage Agent have the most public evidence of working on an existing XDR platform. Simbian, Intezer, and Dropzone document direct connections to CrowdStrike Falcon, Microsoft Defender XDR, and SentinelOne.
Simbian's AI SOC Agent connects to each XDR through its own API. No endpoint agents to deploy. On CrowdStrike Falcon it contains the host, kills the process, blocks the domain, and writes back to the incident. On Defender XDR it isolates devices, disables accounts, and purges malicious email. SentinelOne and Cortex XDR are covered verb by verb on Simbian's integration pages.
Simbian reads from more than 100 tools, the XDR among them, and acts back into 25-plus. One queue works Falcon and Defender estates side by side.
Every action can require sign-off.
As of October 2026, 95% of the responses Simbian proposes are approved by the customer's own analysts. Their call, not ours.
Intezer connects to CrowdStrike, SentinelOne, Microsoft Defender, and Cortex XDR, where it can "auto-resolve false positives within your endpoint tool." We couldn't find the method behind its published verdict figure. Remediation "can be easily automated with explicit human approval."
Dropzone lists CrowdStrike, Microsoft Defender, SentinelOne, and Palo Alto Cortex as alert sources, with 1-click containment, configurable to 0-click. Its docs list remediators for CrowdStrike, Microsoft, Okta, and Google Workspace. We couldn't find one for SentinelOne or Cortex.
Charlotte AI is Falcon's own Agent, and no third-party Agent sits closer to Falcon telemetry. CrowdStrike benchmarks its triage against its own Falcon Complete MDR team, on first-party detections. Containment runs through Falcon Fusion SOAR workflows your team configures. It fits a SOC whose whole estate is Falcon.
Microsoft's Security Alert Triage Agent runs inside Defender. It's generally available for email and collaboration alerts, with some identity and cloud alerts in preview. It resolves false positives and leaves true positives "for an analyst to investigate and take further action." We found no documentation of it triaging non-Microsoft EDR alerts or containing hosts itself.
Also evaluated: SentinelOne Purple AI; Palo Alto's Cortex AgentiX, which claims "host containment across every major EDR platform," naming none we could find; and Stellar Cyber's Open XDR.
An AI SOC Agent should read from XDR and SIEM, then act through the XDR and other tools where containment happens. An XDR correlates telemetry, usually from one vendor's sensors, and responds through them. A SIEM collects logs from every source for search, detection, and retention, and hands response to a SOAR or the XDR.
To watch Simbian act through your Falcon, Defender, SentinelOne, or Cortex tenant, book a demo.
Q: Do I need a third-party AI SOC Agent if I already have Charlotte AI or Security Copilot? Usually, because a native Agent starts from its XDR, and other vendors' evidence mostly reaches it through the XDR vendor's SIEM, data lake, or connectors. A vendor-neutral Agent investigates across all of it and acts back through each XDR with approval.
Q: Can Charlotte AI investigate alerts that don't come from CrowdStrike? Partly, as of October 2026. CrowdStrike documents Charlotte AI Detection Triage as evaluating first-party security detections. Microsoft Defender and SentinelOne data reaches Charlotte AI once ingested into Falcon Next-Gen SIEM, and agentic workflows over that data run in Charlotte Agentic SOAR.
Q: Does Microsoft's Security Alert Triage Agent work with CrowdStrike or SentinelOne? Not according to Microsoft's documentation, which scopes the Security Alert Triage Agent to Defender alerts and the Defender XDR and Microsoft Threat Intelligence plugins. We found no documentation of it triaging CrowdStrike, SentinelOne, or other non-Microsoft EDR alerts.
Q: What is open XDR, and do I need one? Open XDR ingests and correlates telemetry from many vendors' sensors. Stellar Cyber's Open XDR is one example, and adopting it means making Stellar Cyber your platform. A vendor-neutral AI SOC Agent gives similar reach on top of the XDR platform you already run.